Bring requirements, implementation details, and supporting evidence into one shared workspace, keeping your team aligned without disconnected spreadsheets.
Maintain Your System Security Plan
Create and maintain system security plans with organization details, control implementation descriptions, and clear documentation for your team.
Keep Evidence With Your Controls
Attach supporting files to relevant controls, keeping implementation evidence organized and ready for your next review.
Manage Remediation Work
Manage control-linked POA&M tasks with owners, due dates, priorities, and statuses so remediation work has clear next steps.
Track Compliance Progress
Review control status to see which requirements need attention so you can structure your implementation based on your POA&M.
Share Clear Documentation
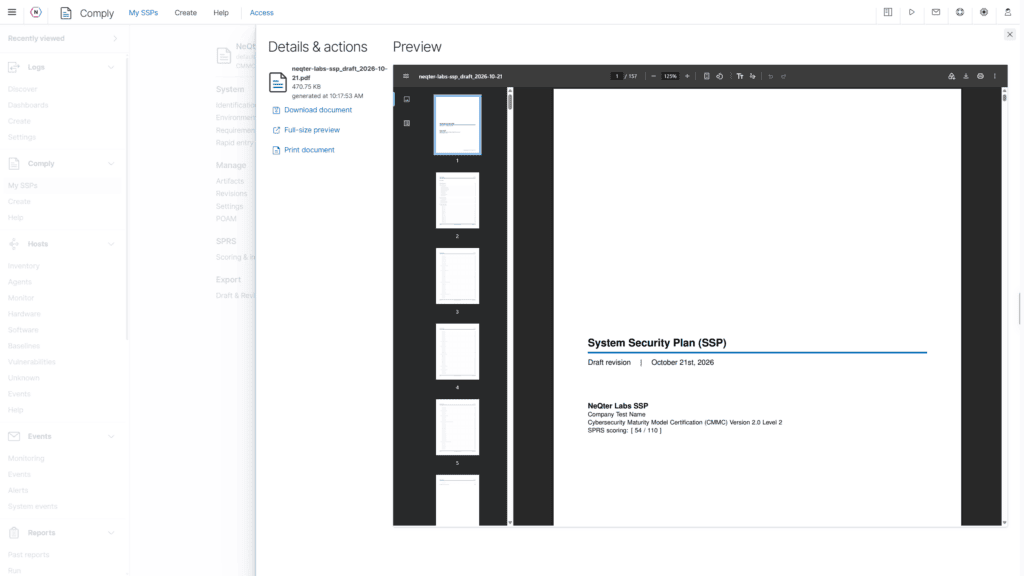
Export SSP drafts, saved revisions, and supporting control details for internal reviews and assessment preparation.
“The NeQter Policy Builder Tools have been instrumental in streamlining our SSP process and made quick and easy work of the ongoing reviews and control updates. The clean, intuitive, efficient and organized layout coupled with control hints and artifact attachments allow us to maintain our SSP in real time with little effort. Absolutely wonderful tool that eases the NIST/CMMC documentation burden.”
- CTO, McLaughlin Research Corporation
COMPLIANCE TRACKING, SIMPLIFIED
Maintain Your Compliance and Stay Audit Ready
The NeQter Comply GRC platform assesses your current security posture, builds and tracks your Plan of Action and Milestones (POA&M), and maintains audit‑ready compliance with CMMC and NIST standards.
ASSESS
Understand Your Starting Point and Identify Gaps
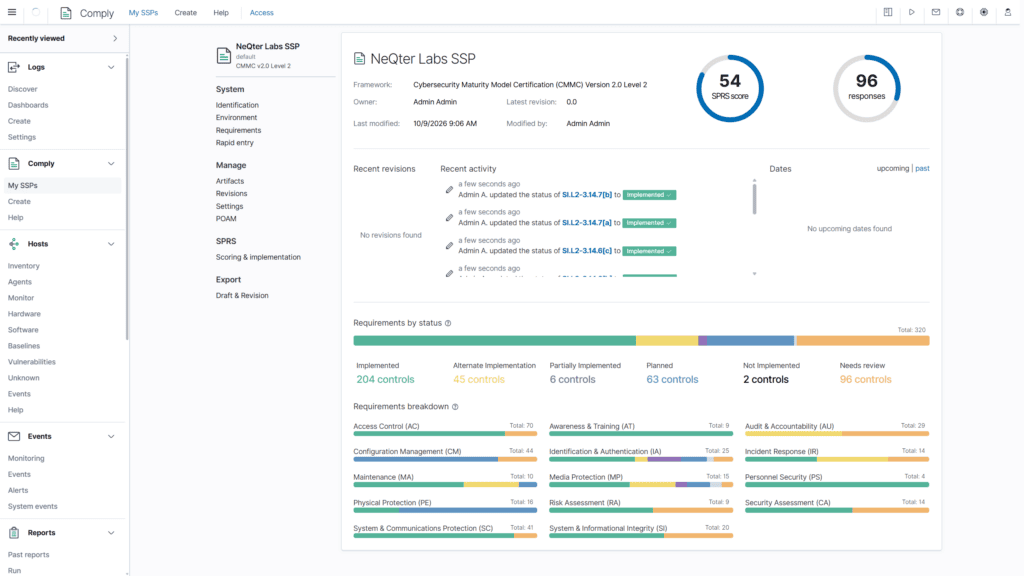
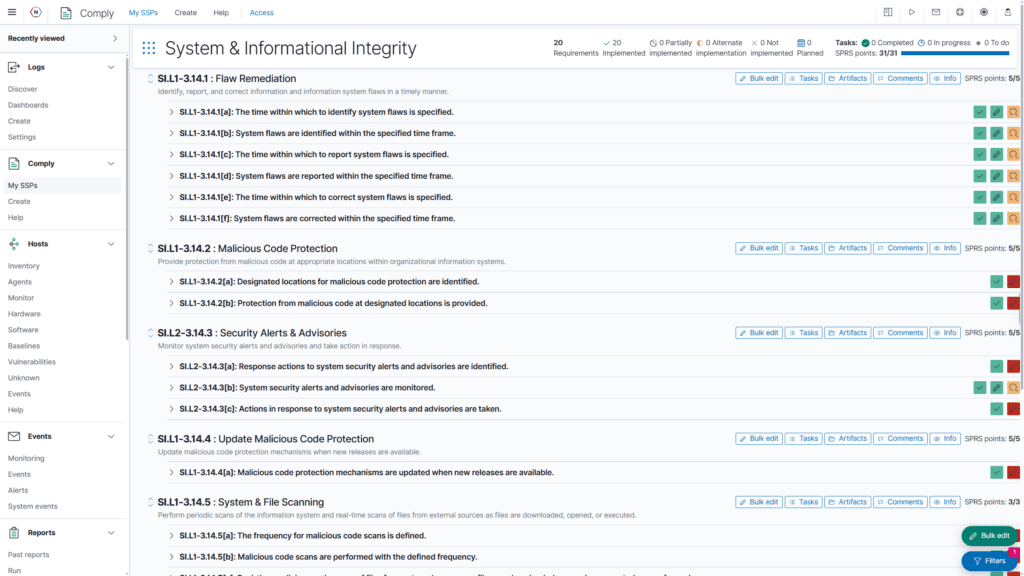
Review control requirements, bulk edit implementation status, and see where your organization needs to focus its compliance efforts.
Review assessment objectives and update implementation statuses individually or in bulk using the Rapid Entry tool.
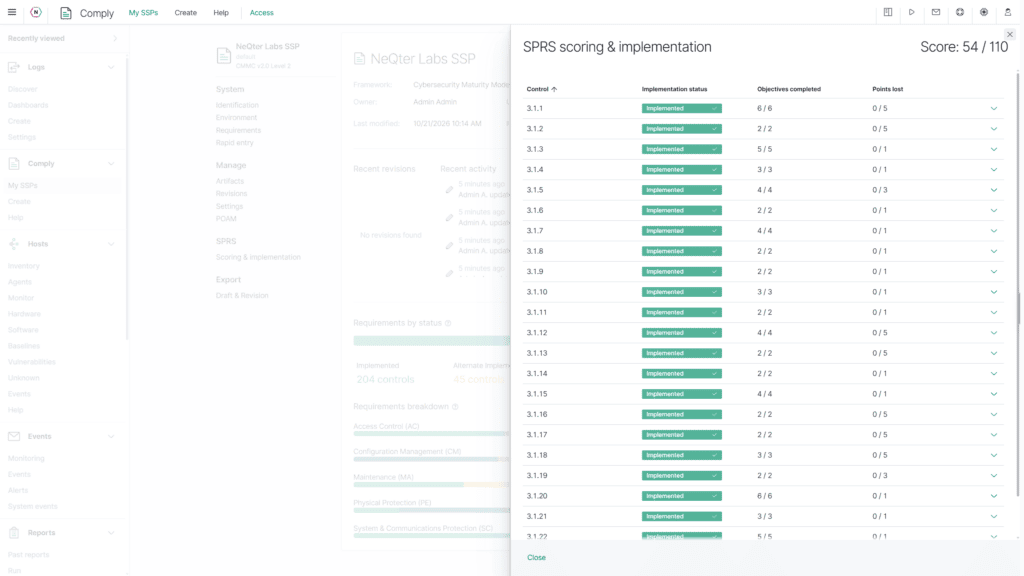
Track implementation progress by control family and, for supported frameworks, review an SPRS score calculated from the implementation statuses your team has recorded.
PLAN
Turn Compliance Gaps Into Clear Next Steps
Organize remediation work around your controls, with clear ownership and deadlines that help your team move forward.
Create control-linked POA&M tasks with owners, priorities, and due dates to make remediation responsibilities clear.
Keep planned work in one POA&M view, review task statuses, and update individual items as your team addresses gaps and documents the actions taken.
PROVE
Bring Your Evidence and Documentation Together
Keep supporting files alongside control implementation details, making your documentation easier to organize, review, and share when needed.
Upload supporting files and attach them to relevant controls so evidence stays connected to your implementation descriptions.
Export SSP drafts, saved revisions, and supporting control details for internal reviews or assessment preparation, giving stakeholders a clearer view of the documentation your team maintains.
MAINTAIN
Keep Compliance Documentation Current as Things Change
Update system details, revisit implementation descriptions, and preserve SSP revisions as your organization and compliance work evolve.
Review requirements needing attention and update implementation statuses, descriptions, and supporting artifacts as circumstances change.
Save SSP revisions to retain earlier versions, then revisit documentation and update open tasks as your organization changes, keeping your compliance records useful beyond the initial assessment.
Ready to protect your business, achieve compliance and win and retain contracts?
NeQter is the fastest, most comprehensive way to defend your business reputation, protect your customers’ proprietary information and achieve CMMC compliance.
Talk to us today, and let’s explore what NeQter Labs can do for your organization.